The Cost of Memory Unsafety
Reduce Risk. Protect Investment. Build Trust.
From emergency patches and delayed releases to service disruption and loss of trust, memory-unsafe software can affect organisations long after a product ships.
CHERI helps reduce that risk by making many memory-safety errors impossible to exploit and limiting the impact of those that remain.
The Hidden Cost of Memory Vulnerabilities
When a memory-safety vulnerability is found, fixing the bug is often the smallest part of the cost.
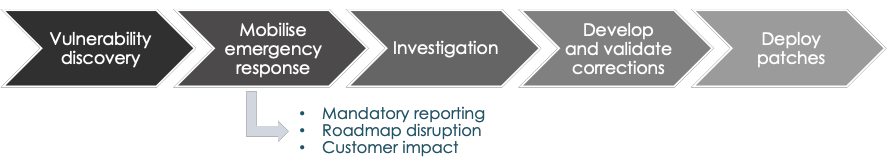
A memory-safety vulnerability can trigger costly investigations, regulatory reporting, emergency patching, customer support activity, compliance work, and roadmap delays, consuming resources long after the original bug has been fixed.
Even when no attack occurs, the investigation and remediation effort consumes time, resources, and budget. Even worse, with incoming regulations (including the Cyber Resilience Act in Europe), there is an obligation and pressure to fix problem in a given time, potentially disrupting development roadmaps.
A recent study showed that 21 new Linux vulnerabilities are discovered per day… This is worth investigating new solutions!
Why This Matters Now
Memory-safety vulnerabilities continue to account most serious software vulnerabilities.
At the same time:
- software is becoming more connected
- products remain deployed for longer
- regulatory expectations are increasing
- governments are placing greater emphasis on memory safety and secure-by-design practices
For many organisations, reducing memory-safety risk is becoming a strategic objective rather than simply an engineering concern. This is highlighted in CISA’s case for memory-safe roadmaps.
What CHERI Changes
From Mitigating Attacks to Preventing Them
Traditional defences often just make memory vulnerabilities harder to exploit, until attackers find how to bypass them. CHERI changes the model.
By enforcing memory access rules directly in hardware, CHERI can prevent many invalid memory accesses from succeeding in the first place.
Combined with compartmentalisation, CHERI can also limit how far an attacker can move when a component is compromised.
Key benefits
- Reduce exposure to memory-safety vulnerabilities
- Limit the impact of software compromises
- Protect existing C and C++ investments
- Improve resilience of long-lived products
- Support secure-by-design strategies
The Business Outcome
Spend Less Time Responding. Spend More Time Innovating.
The goal is not simply to prevent individual vulnerabilities. It is to reduce the operational burden that memory vulnerabilities create throughout a product’s lifecycle.
By helping organisations detect faults earlier, contain compromises, and protect existing software investments, CHERI can help teams:
- reduce security risk
- improve product resilience
- simplify long-term support
- maintain customer trust
- focus resources on innovation rather than emergency response